PHP2Shell: Critical PHP RCE Vulnerabilities (Oct 2026)
In October 2026 two critical PHP engine bugs (“PHP2Shell”) were disclosed. These unauthenticated memory-corruption flaws allow remote code execution on affected servers. If your site runs PHP, patch immediately.
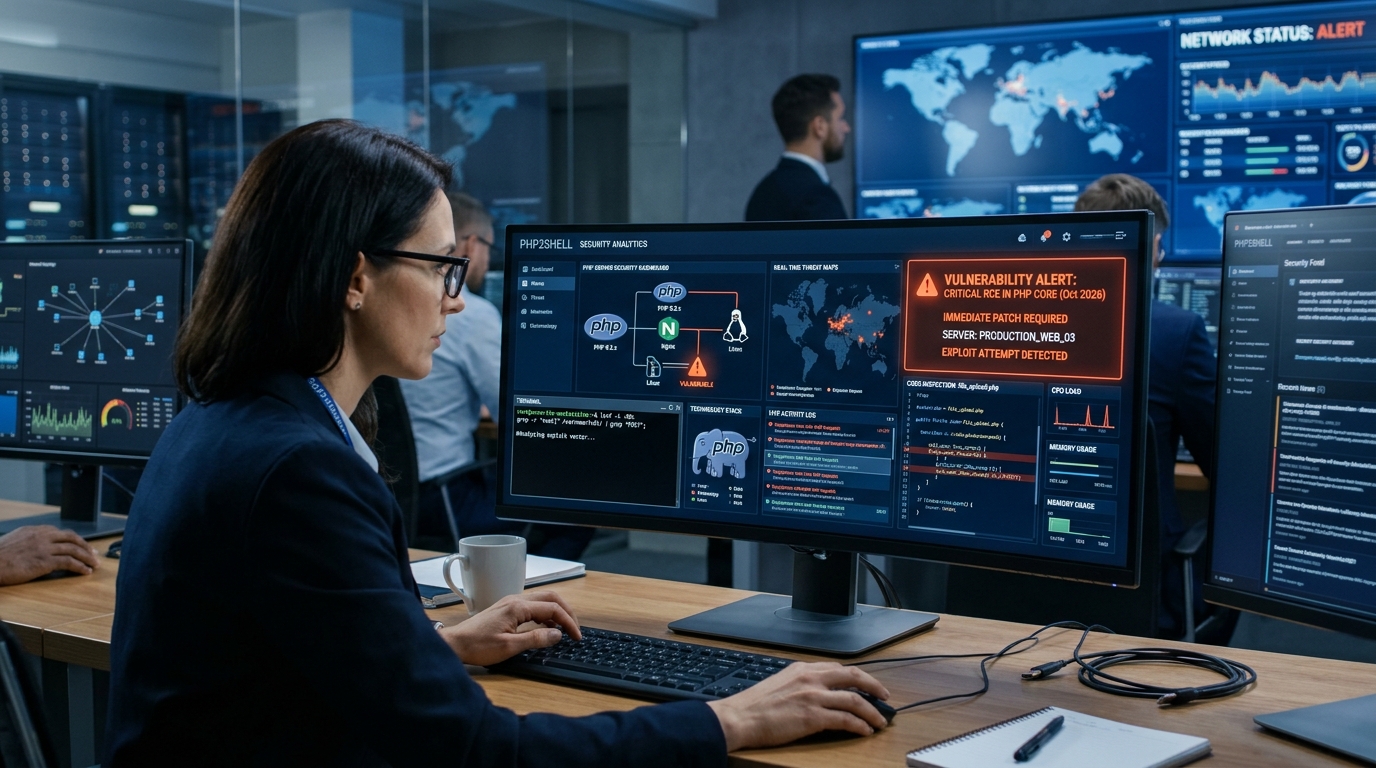
On October 21, 2026, the PHP Project released emergency security updates to fix two severe memory-safety flaws in the PHP runtime. Collectively nicknamed “PHP2Shell,” these vulnerabilities allow an unauthenticated attacker to execute arbitrary code on any vulnerable PHP server. The PHP advisory rates both CVE-2026-109618 and CVE-2026-109619 at 9.2/10 severity. In practical terms, an attacker could remotely run malicious PHP on your site without logging in, putting all your data and web infrastructure at risk.
Affected Versions and Impact
These bugs affect nearly every PHP installation. Officially, all PHP releases from 5.4 up to 8.5.11 are vulnerable. This includes common setups like Apache (mod_php), PHP-FPM, PHP-CGI, and even modern hosts like FrankenPHP or LiteSpeed. Popular web platforms – WordPress, Drupal, Joomla, Magento, Laravel, and more – are at risk because the flaw lies deep in PHP’s engine, not in any one application. Researchers at security firms like Wiz demonstrated that both simple “Hello World” scripts and full CMS installations are exploitable. In short, any website running an unpatched PHP version could be taken over. This is a very urgent situation: the PHP advisory explicitly warns “All PHP users are strongly encouraged to update immediately.”
How PHP2Shell Works (Overview)
PHP2Shell actually consists of two related bugs in PHP’s memory handling when processing requests. Both can lead to Remote Code Execution (RCE):
- CVE-2026-109618 (OOM Corruption): When PHP runs out of memory, it aborts the request. Under certain conditions, the abort sequence leaves internal PHP state partly corrupted. During cleanup, PHP may incorrectly treat garbage data as valid, allowing attacker-controlled input to execute as code.
- CVE-2026-109619 (Stale Memory State): PHP handles many requests per process. Sometimes, when cleaning up after a request, old memory data isn’t fully cleared. A malicious new request can trick PHP into reusing that stale memory in a dangerous way, effectively hijacking execution flow.
Both bugs were independently discovered by security researchers using advanced tools (including AI models). Notably, firms like Wiz Security and Calif Security used state-of-the-art language models (OpenAI’s GPT-5.6 and Google Gemini) to find these flaws. The combination of these bugs means an attacker can craft requests that overflow or leak PHP’s memory, injecting arbitrary code for execution. In experiments, the researchers successfully demonstrated full server takeover, data leaks (passwords, keys), and site defacement on unpatched systems.
Immediate Patching and Mitigation
Apply official patches now. On October 21, 2026, the PHP team released fixed versions: PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35. These updates correct the memory-corruption bugs. If you manage your own server or container, update PHP immediately via your package manager or rebuild with the new PHP binaries. If you use managed hosting (cPanel, Plesk, WordPress hosting, etc.), contact your provider or use their control panel to upgrade PHP. Do not delay – attackers are already probing the web for unpatched sites.
- Self-managed servers/containers: Run your system’s update (apt/yum/… ) or rebuild your Docker images with the new PHP version. Verify the update with
php -v. - Hosted environments: Check notices from your host. Many cloud providers (Google App Engine, AWS, DigitalOcean, etc.) have announced automatic updates or provided new platform images. Apply the latest runtime or OS updates they offer.
- Legacy PHP (<8.2): PHP versions 8.1 and earlier are end-of-life and not officially patched. If you are on 8.1 or below, you must upgrade to at least 8.2. Alternatively, see if your provider offers a backported security update, but that should be a last resort.
If you cannot patch immediately, consider these temporary mitigations: disable PHP features like session.upload_progress and reduce memory_limit settings in php.ini. These steps make exploitation harder but do not fully fix the vulnerability. The only reliable remedy is the official PHP update.
Action Checklist for Site Owners
Treat PHP2Shell like a critical emergency:
- Identify all PHP environments: Find every server, container, or process running PHP. Don’t overlook development, staging, or cron jobs.
- Back up your data: Take current backups of your code and databases before applying changes.
- Test updates safely: Patch PHP on a non-production copy of your site first. Ensure everything works before updating live servers.
- Apply patches to production: Roll out the patched PHP versions to all production servers. Verify the update and restart PHP services as needed.
- Scan and monitor: After patching, run vulnerability scans or intrusion detection. Check server logs for suspicious requests around Oct 20–28, 2026. Enable or update your WAF rules to watch for PHP2Shell exploit patterns.
- Inform stakeholders: If you manage or develop sites for clients or others, notify them of the issue and the patch schedule. Emphasize that this is a high-severity, zero-day vulnerability, and communicating promptly can prevent panic.
Acting quickly and methodically will greatly reduce your risk. Even if your site hasn’t been attacked yet, assume a breach could happen any time. For extra peace of mind, consider running a security audit or malware scan after updating.
How Lishaq Solutions Can Help
Dealing with PHP2Shell and other emergencies is exactly what we do. Lishaq Solutions offers expertise in securing PHP applications and servers. We can:
- Apply emergency patches: We’ll update your PHP environment safely and test your site to ensure no compatibility issues.
- Audit and harden: Our team can review your code and server settings, disable unused features, and implement best practices to prevent future breaches.
- Respond to incidents: If you suspect an intrusion or defacement, we provide rapid cleanup and recovery to get you back online securely.
- Managed hosting: Our hosting plans include proactive updates and monitoring, so you’re automatically protected from known vulnerabilities like PHP2Shell.
Don’t leave your website exposed to this critical flaw. Contact us today for immediate assistance in patching and securing your PHP site. Discuss Your Project →
Frequently Asked Questions
Q: Does PHP2Shell mean I should switch away from PHP?
A: No. Every technology can have vulnerabilities. The PHP2Shell bug lies in the PHP engine’s memory handling, and it has been addressed. Once patched, your PHP site is as secure as any other. The important thing is to stay current with updates on any platform.
Q: My host says they patched their servers. Can I trust that?
A: Hosts should provide specifics. Check if their updated PHP version is at least 8.2.35+ (or higher) or an official backport of the fixes. If unsure, ask for a version number. If possible, verify by running a small PHP script that outputs phpinfo() on your site.
Q: How can I tell if my site was attacked?
A: Look for unusual logs and file changes. Common signs include unexplained admin accounts, new PHP files, or odd requests in your web logs around Oct 20–28. We also recommend scanning the server with a security tool. We can assist in thoroughly checking for any compromise.
Q: Is there any way to detect PHP2Shell attempts?
A: Some Web Application Firewalls (WAFs) have rules for PHP2Shell patterns. For example, requests with unusual memory syntax or large payloads. The free OpenAI checker (on GitHub) can also identify vulnerable versions. Ultimately, patching is the detection-free fix.